
Vendor relationships are at the heart of every procurement operation—but they come with risk. In 2026, managing vendor risk manually is not only inefficient but also increasingly dangerous. With new cybersecurity threats, ESG regulations, and global supply chain volatility, businesses must evolve their approach to vendor oversight.
That’s why leading procurement teams are prioritizing how to automate vendor risk management across their workflows. By embedding automation into your vendor lifecycle—from onboarding to performance monitoring—you reduce exposure, save time, and stay audit-ready.
In this article, we’ll explore how to automate vendor risk management using modern tools and practical strategies, and how you can future-proof your supply chain by doing so.
What Is Vendor Risk Management?
Vendor risk management (VRM) is the process of identifying, assessing, monitoring, and mitigating risks that stem from third-party vendors, suppliers, or partners. These risks include:
- Cybersecurity vulnerabilities
- Regulatory and compliance risks
- Operational disruptions
- Financial instability
- Reputational damage
In 2025, organizations are expected to manage not only traditional risks but also new layers of complexity, such as:
- ESG reporting requirements
- AI-powered vendor tools with unknown risk models
- Real-time threat alerts
- Cross-border data privacy compliance
The only way to keep pace with these demands is to automate vendor risk management using intelligent systems that can monitor, score, and respond to risk without manual input.
Why Automate Vendor Risk Management?
Businesses that automate vendor risk management gain a significant advantage in terms of speed, compliance, and resilience. Here’s why:
1. Proactive Risk Detection
Automated tools can scan global data sources, supplier certifications, and regulatory alerts in real time—flagging potential issues before they become liabilities.
2. Streamlined Compliance
With built-in audit trails and dynamic risk scoring, automation ensures you remain compliant with laws like GDPR, CCPA, SOX, and ISO standards—without chasing paperwork.
3. Faster Vendor Onboarding
AI tools can instantly analyze vendor data, assess risk profiles, and approve low-risk vendors in hours instead of days—shortening procurement cycles significantly.
4. Lower Operational Costs
Instead of hiring more compliance analysts, automation allows your existing team to scale monitoring across hundreds of vendors efficiently.
5. Real-Time Dashboards and Reporting
Centralized dashboards provide real-time visibility into vendor risk levels across all categories—financial, cybersecurity, ESG, legal, and more.
Key Features in Automated Vendor Risk Management Systems
To effectively automate vendor risk management, your system should include:
- Centralized Vendor Profile Management
All vendor information, documents, risk scores, and certifications should be stored in one accessible platform.
- Real-Time Risk Monitoring
Integrations with third-party databases (e.g., credit bureaus, news aggregators, compliance feeds) enable continuous risk scoring and alerts.
- Automated Workflows & Escalations
Trigger automatic reviews, approval gates, and alerts when high-risk indicators arise—no manual follow-ups needed.
- AI-Powered Risk Assessments
Machine learning algorithms assess vendor documents, contracts, and performance data to assign dynamic risk scores.
- Configurable Dashboards
Filter vendors by risk level, region, compliance status, or contract value—so you always know where to focus.
How to Automate Vendor Risk Management: Step-by-Step
Here’s a simplified roadmap to get started with automation:
Step 1: Define Your Risk Categories
Identify which vendor risks are most relevant to your business—e.g., cyber, ESG, financial, or reputational. Define your tolerance levels.
Step 2: Categorize Vendors by Risk Tier
Segment vendors based on criticality and risk exposure. This will guide how often each group is reviewed or monitored.
Step 3: Choose the Right Automation Platform
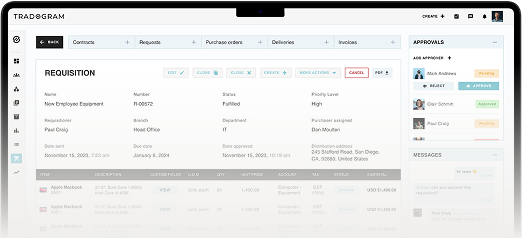
Use a procurement platform like Tradogram that integrates risk monitoring, vendor scoring, and compliance tracking in one place.
Step 4: Automate Onboarding and Due Diligence
Configure automatic document checks, KYC validations, and risk scoring during onboarding using AI tools and pre-set criteria.
Step 5: Set Risk Triggers and Escalation Paths
For example, if a vendor’s credit rating drops below a certain level or ESG compliance is overdue, the system should flag it and notify your team.
Step 6: Review and Improve Regularly
Use built-in analytics to identify recurring issues, improve scoring logic, and adapt to new risk factors.
Tools That Help Automate Vendor Risk Management
Several tools and platforms can help automate vendor risk management processes. Look for solutions that offer:
- API integrations with external risk intelligence sources
- Contract lifecycle management with compliance tracking
- Automated audit logs and documentation
- Support for ESG, cybersecurity, and data privacy frameworks
- Real-time collaboration between procurement, legal, and finance teams
Tradogram offers a fully integrated vendor management system with customizable risk workflows, vendor performance tracking, and document automation—ideal for mid-size to enterprise-level organizations.
Conclusion: Future-Proof Your Risk Strategy
As third-party risk continues to rise, businesses must shift from manual, reactive processes to automated, proactive systems. Learning how to automate vendor risk management isn't just a trend in 2026—it’s a requirement to stay compliant, resilient, and competitive.
By investing in automation, you’ll not only reduce vendor-related incidents but also increase transparency, strengthen relationships, and free up your procurement team to focus on strategic work.
Ready to Automate Your Vendor Risk Management?
Tradogram can help. Explore our vendor management solution or book a demo to see how automation can secure and streamline your procurement process.